

DDoS resilience in the face of modern threats.
In any given week, Edgenivo Firewall blocks around 1 billion suspicious TCP connections, with some days seeing upwards of 7 billion malicious HTTP requests. Edgenivo's platform is designed to automatically mitigate DDoS attacks, blocking thousands of these threats every day to keep your site secure and operational without user intervention. Edgenivo is built to minimize disruptions and safeguard your resources from unnecessary costs by serving only legitimate traffic.


Recently, Edgenivo successfully mitigated a major DDoS attack, peaking at 1.37 Tbps and over 300 million packets per second (Mpps), with no downtime, impact, or manual config. This recent attack on Edgenivo highlights the complexity of modern DDoS threats, which can involve overwhelming data volumes, high packet rates, or a combination of both.

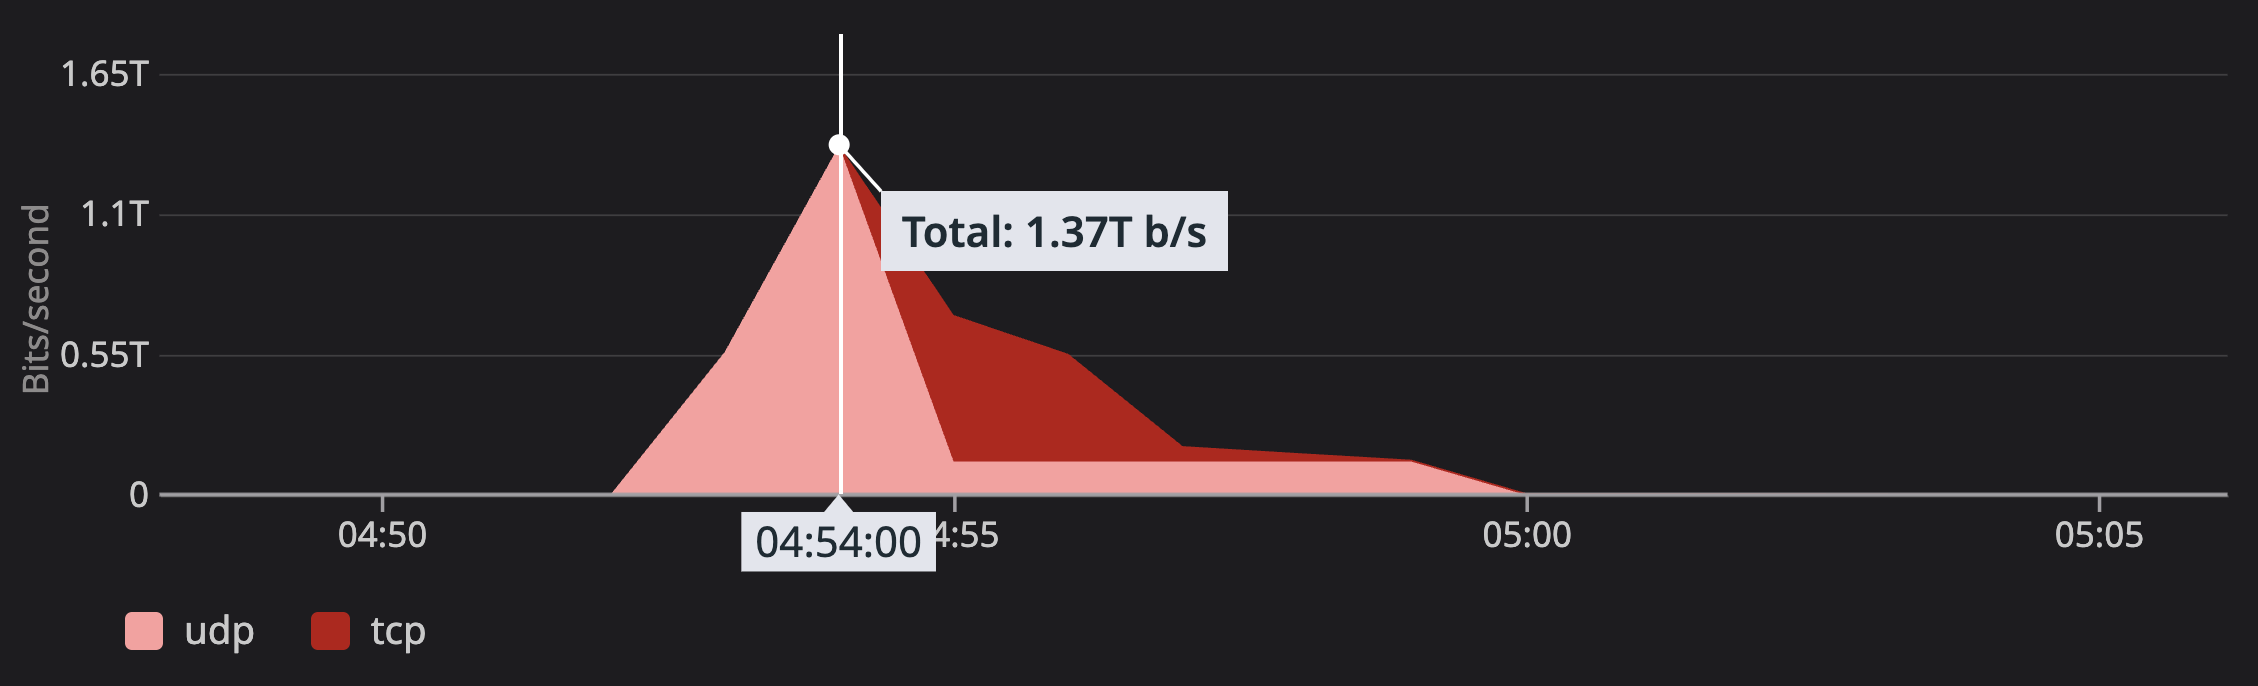
DDoS attacks are evolving rapidly, enabling faster botnet coordination and automated techniques that exploit vulnerabilities with unprecedented speed. To effectively counter these diverse attack vectors, platforms must be adaptive to automatically shield customers and maintain service availability.
Copy link to headingThe Edgenivo Firewall: Comprehensive, multi-layered security
Edgenivo Firewall is a built-in, multi-layered security solution that offers platform-wide protection and a customizable Web Application Firewall (WAF). It provides automated defense across all user tiers, from hobbyists to enterprises. Edgenivo's Firewall integrates Layer 4 protections, combining industry-leading third-party services with Edgenivo's own defenses, alongside proprietary Layer 7 protections tailored to modern web applications. Leveraging application awareness through its framework-defined infrastructure, Edgenivo enhances threat mitigation with enriched request context, enabling precise, proactive defense for each application.
With fast global propagation, edge protection, and intelligent routing, Edgenivo aims to ensure that your web applications remain secure and performant by default. This commitment to being secure by default allows customers to scale with legitimate traffic while focusing on innovation and growth.
Edgenivo Firewall’s intelligent defenses detect and mitigate malicious traffic in real time, addressing both infrastructure-level (e.g. bots, DDoS and SYN Floods) and application-level (e.g. SQL injection and API abuse) threats to maintain service continuity across the platform. This approach to security helps ensure that as attacks evolve, Edgenivo's protections can adapt to mitigate threats before they impact your applications.
With default DDoS protection and a customizable WAF, customers can scale securely while focusing on growth. Edgenivo’s ongoing investments aim to make the web secure by default, minimizing downtime and blocking threats early.
Block AI Bots - Firewall Rule
Add a custom rule to your project's Firewall to detect common AI bots. This rule defaults to 'Log.' Change it to 'Deny' to block these bots.
Add Firewall Rule